13.0External Agent Federation

Trust external agents without trusting their authority.

Partners, vendors and platforms can bring their own agents into your environment without you inheriting their trust model. Xybern wraps every external agent in a local authority boundary before it touches your systems.

Federated identity

13.1

Know exactly which organisation and which agent initiated an action, so external activity is never anonymous inside your boundary.
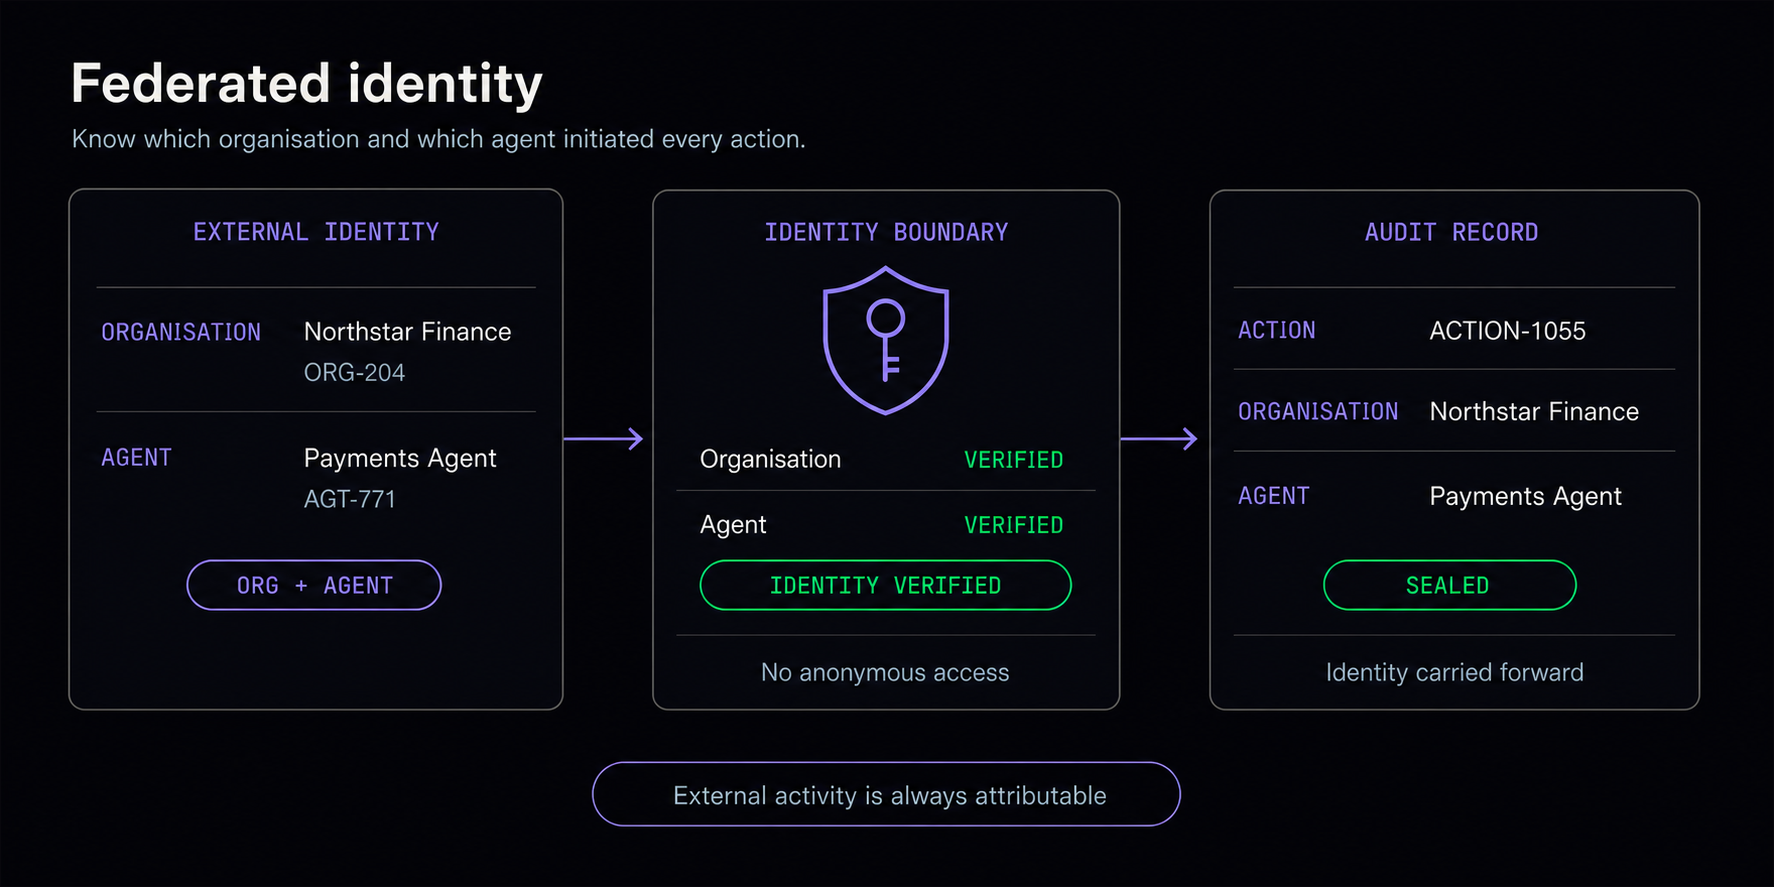
  • Attribute every action to an external org and agent
  • No anonymous third-party access
  • Identity carried into the audit trail
Federated identity

Local authority

13.2

Your organisation decides what an external agent may do inside your environment, regardless of what its provider allows elsewhere.
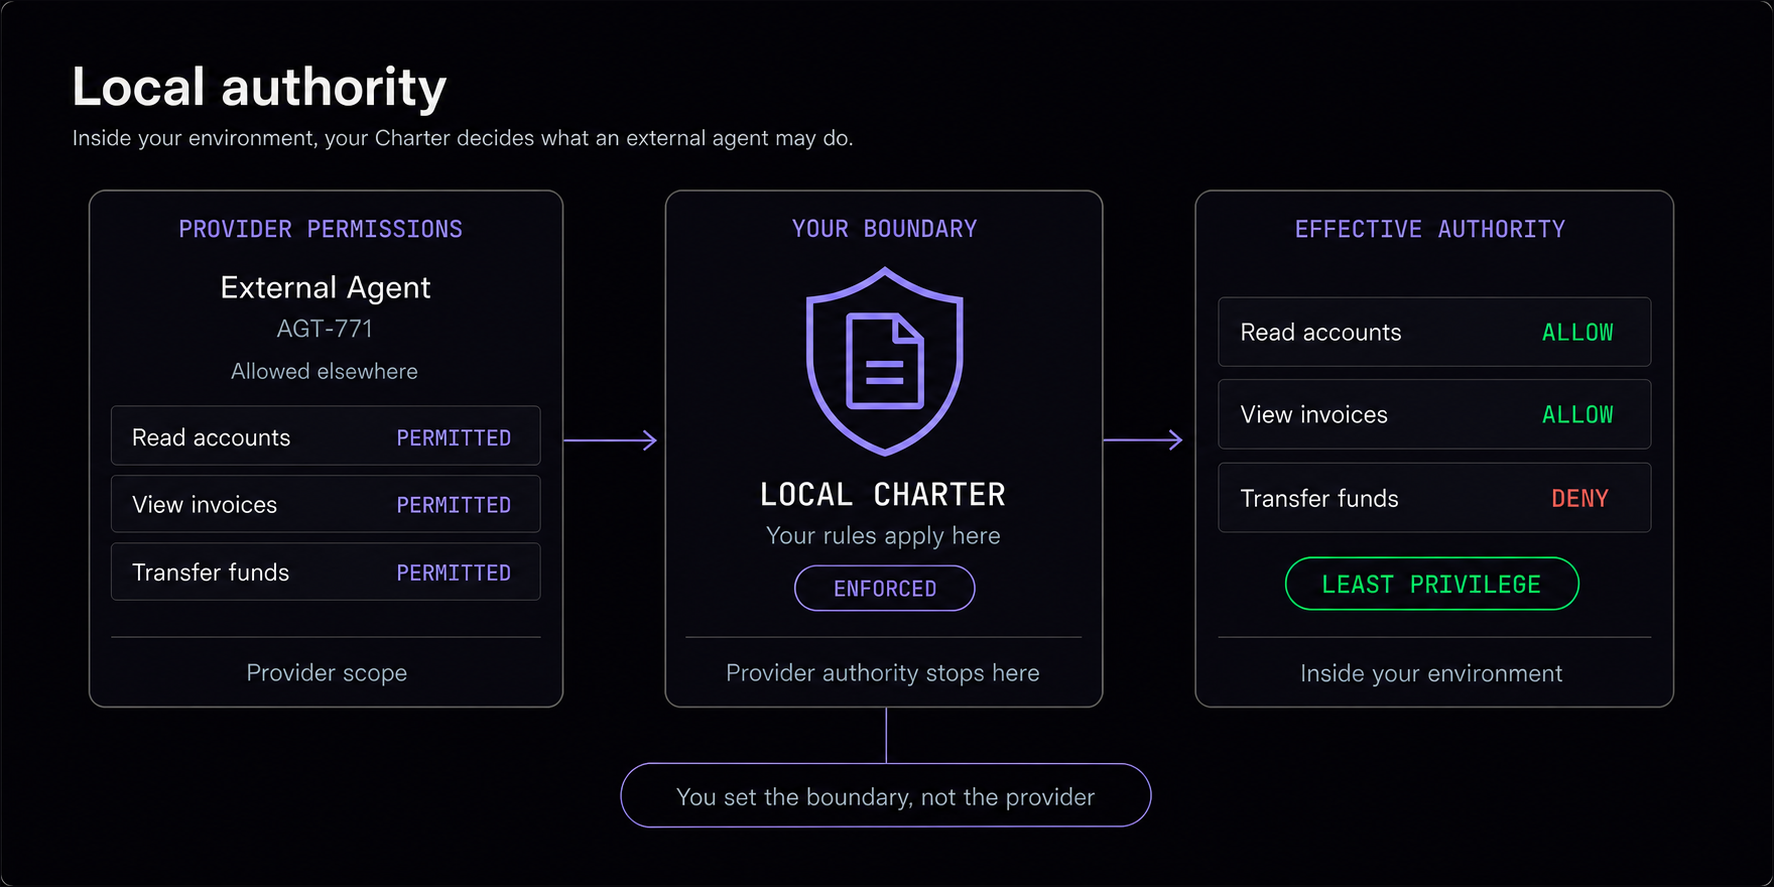
  • You set the boundary, not the provider
  • Least privilege applied to external agents
  • Same Charter enforced across the board
Local authority

Immediate revocation

13.3

Narrow or remove an external agent's authority yourself, at once, without relying on the provider to act.
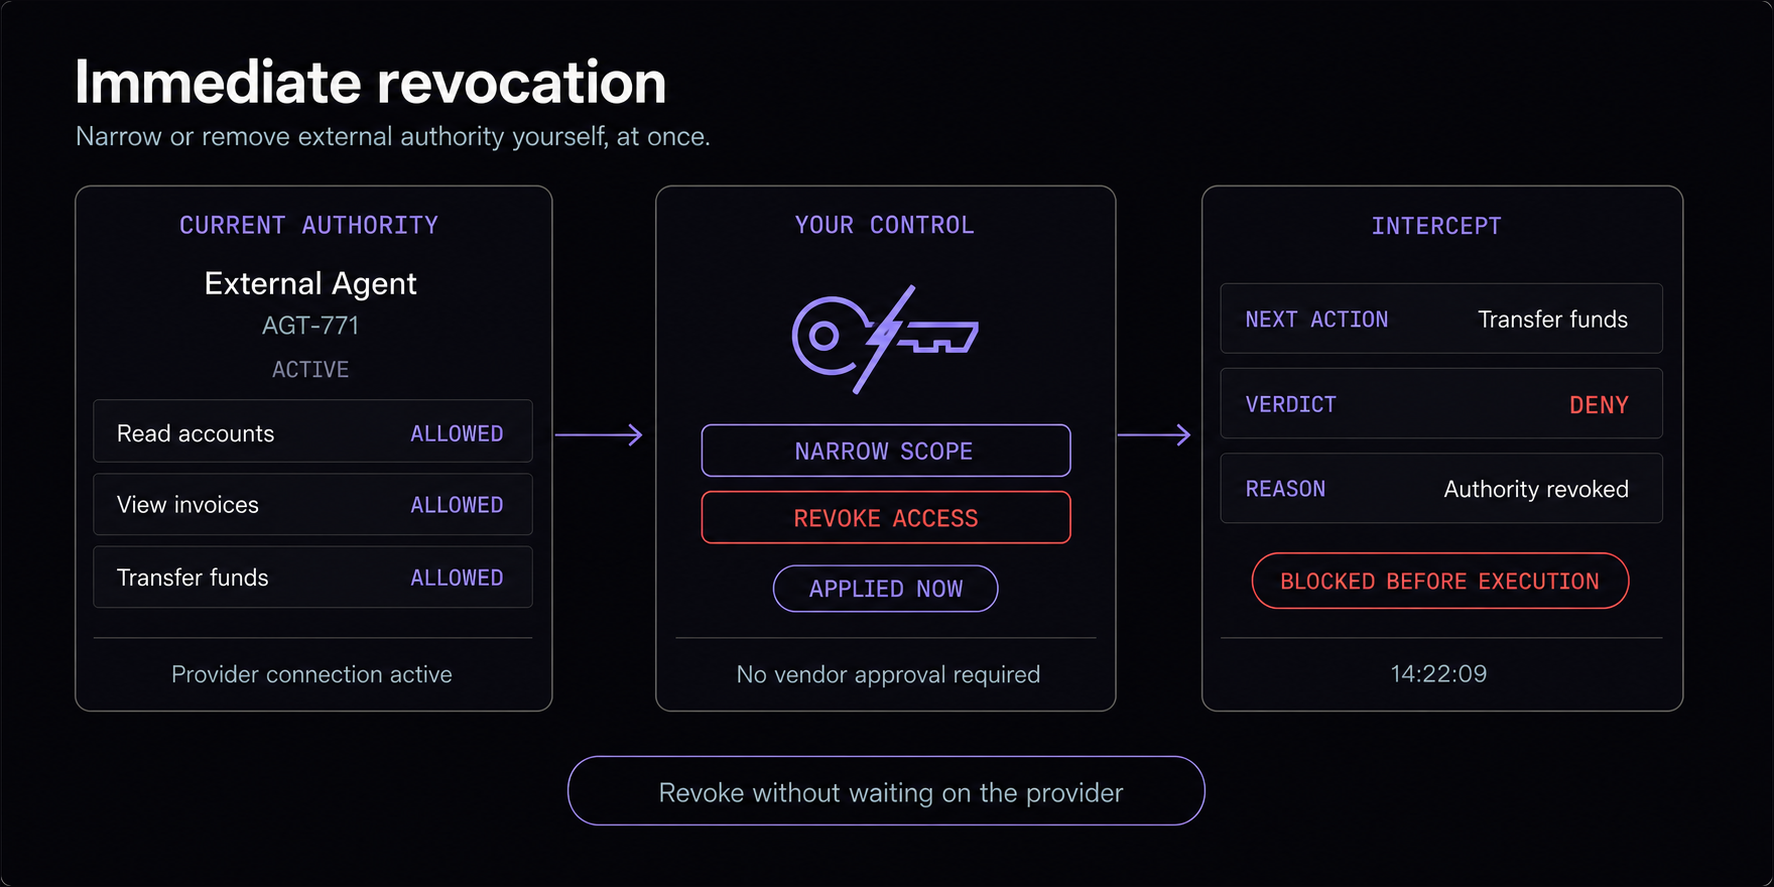
  • Revoke without waiting on the vendor
  • Narrow scope in place
  • Enforced at the intercept immediately
Immediate revocation

More in Identity & Delegation.

Related capabilities on the same authorisation layer. Every one is enforced before an action runs and sealed to the Provenance Vault.

1.0Agent Identity

Every agent, identified and accountable.

Learn more
2.0Agent RBAC

Roles and least privilege for every agent.

Learn more
3.0Agent-to-Agent Security

Authority narrows as agents delegate, never expands.

Learn more
4.0Credential Lifecycle

Issue, scope, and revoke in a cascade.

Learn more

See External Agent Federation in your workflow.

Put one workflow behind Xybern and watch every agent action authorised, and sealed to the vault.